
Scattered
The answer to one audit question sits in three tools and two inboxes. Nobody owns collecting it.
IT OPERATIONS
Unified360IT operations & observability platformNetwork TopologyAuto-discovered mapsLink UtilizationBandwidth and link qualityBusiness Service ManagementApplications, services and impactIPAMSubnets, IPs and conflictsAlerting & EscalationDetect, notify, recoverSERVICE & ASSETS
ITDeskIT service management platformIncidents & SLAsOne desk for every requestIntelliAssetIT asset & patch managementPatch ManagementDetect, deploy, roll backISMS Audit PackISO 27001 evidence, readyBY CHALLENGE
Blind Spots in InfrastructureNo extra tools: hardware to URLs on one screenSlow Ticket ResolutionRoute, watch and escalate to fix fasterUnknown Assets & Unpatched SystemsKnow what you own, patch what's exposedUncontrolled Privileged AccessVault, approve, record and auditManual, Repetitive OperationsAutomate approvals and remediationAudit & Compliance PressureEvidence on demandBY STACK
Networks & WirelessSwitches, firewalls and controllersServers & DatabasesWindows, Linux and leading databasesVirtual & Hybrid EstatesHypervisors and hybrid workloadsEndpoints & DevicesAgent-based inventory and updatesRemote & Privileged SessionsAgentless SSH, RDP and VNCTools & IntegrationsITSM, SIEM, webhooks and emailLEARN
Quick Start GuidesSoonGet productive with any Autointelli product in minutes.Product DocumentationAdmin manuals, how-tos and API references.Integration CatalogSoonWhat Autointelli connects to, and how.IT Terms ExplainedPlain-language definitions of everyday IT jargon.DISCOVER
Customer StoriesHow organisations get measurable results.WhitepapersResearch on IT operations, ITSM, ITAM and PAM.Ebooks & PlaybooksPractical, step-by-step operating guides.Product DatasheetsCapabilities and technical specifications.Why AutointelliHow we differ from other platforms.Compare AutointelliSide-by-side with tools you may be weighing.Solution · By Challenge
Audits rarely fail on the controls. They fail on the evidence: who owned the asset, what was patched, who approved the change, who logged in. Autointelli keeps that evidence as a by-product of running IT, so an audit is an export, not a hunt.
The problem
The work was done. Proving it is where the pressure comes from.
The answer to one audit question sits in three tools and two inboxes. Nobody owns collecting it.
Spreadsheets are out of date the day they are saved. By the time an auditor reads them, they describe last quarter.
You can say a control works, but you can't show who did what, when, or which controls have nothing behind them at all.
Where the pressure comes from
How it goes wrongAn asset list that was accurate the day someone saved it, with owners nobody has confirmed.
Closed withIntelliAsset keeps the register from discovery and agents, with custody and transfer logs and physical verification campaigns. The Master IT Asset Register maps to Annex A 5.9.
How it goes wrongEach machine has its own answer, and nobody can show the fleet.
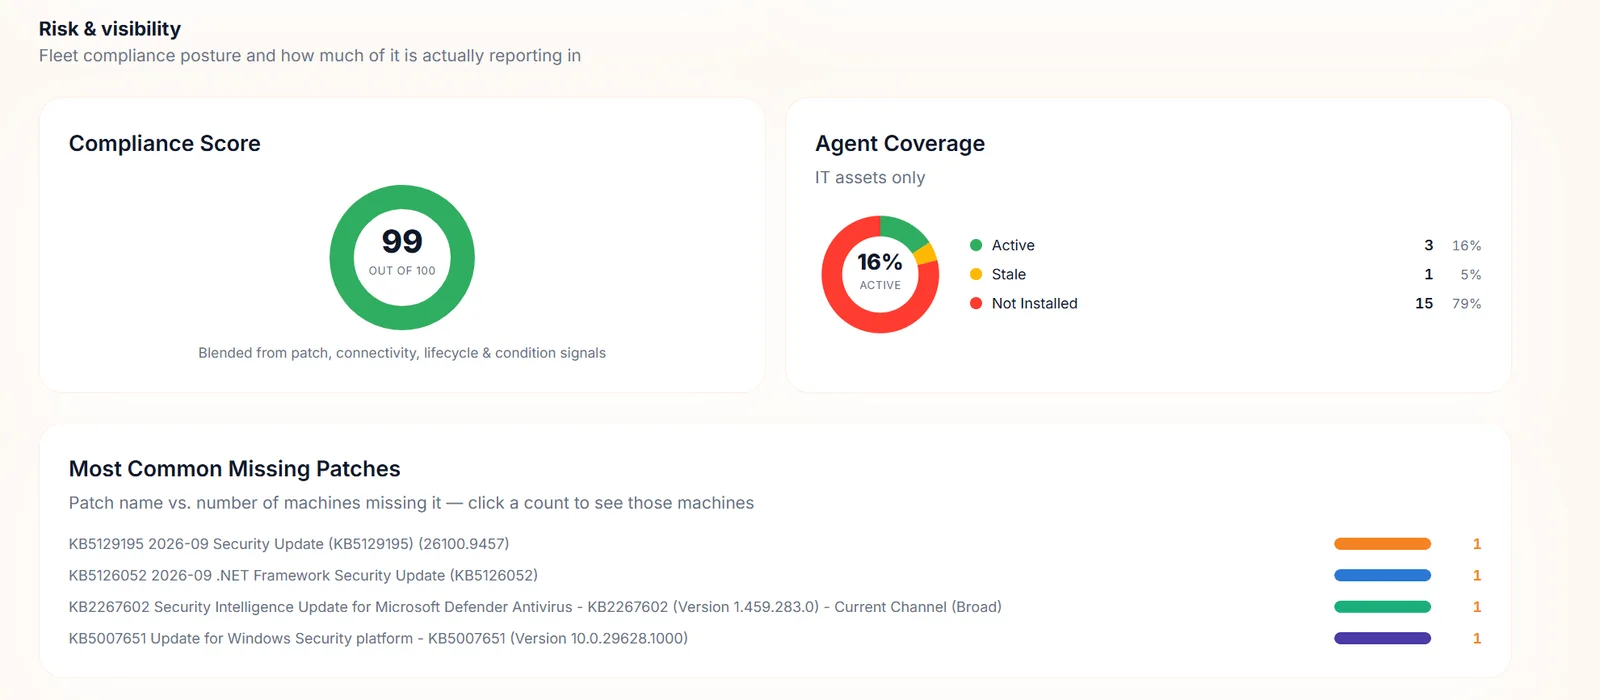
Closed withPatch Compliance Summary, Critical Vulnerability Exposure and Patch Deployment Change Log, mapped to control 8.8, with a compliance score per device.
How it goes wrongLogs live on individual servers, and half of them were never kept.
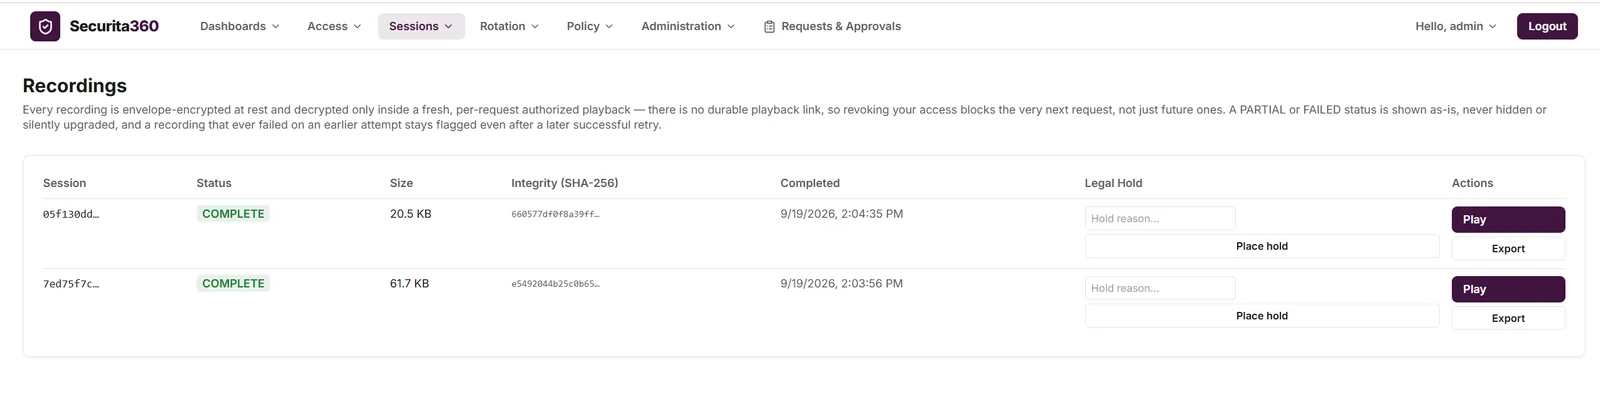
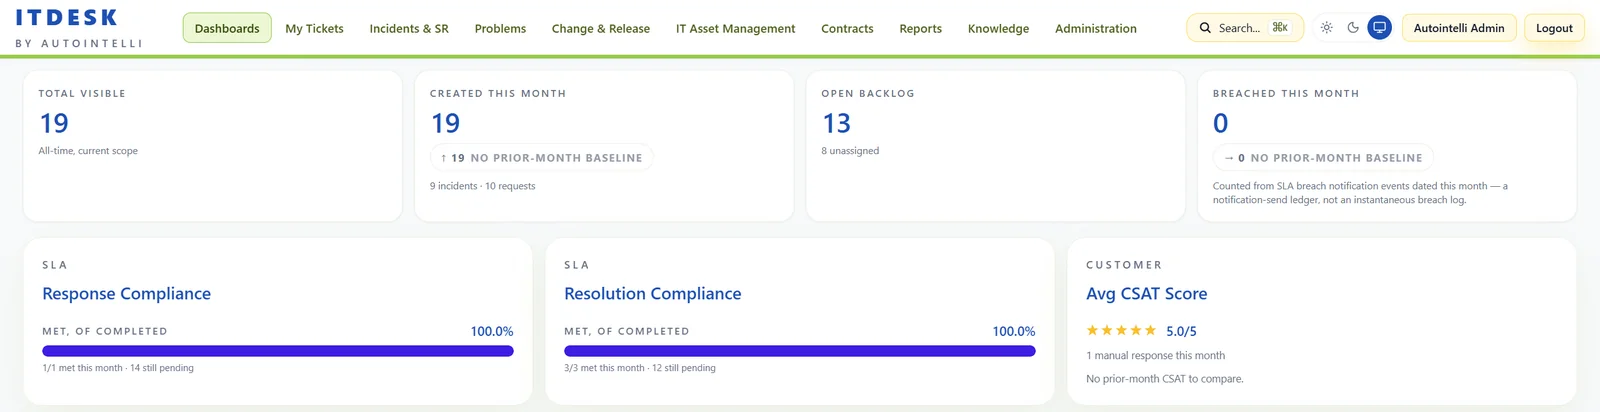
Closed withAudit trails that name the actor, the action and the time: IntelliAsset's platform trail, ITDesk's system log, Securita360's hash-chained trail with recordings, and Unified360's alarm and run history.
How it goes wrongA change was made. Who approved it, and was it checked afterwards?
Closed withITDesk records each CAB approval with the decision, note and time, plus a post-implementation review. IntelliAsset logs patch deployments, and Unified360 compares config snapshots.
How it goes wrongThe week before an audit disappears into exports, screenshots and pasted tables.
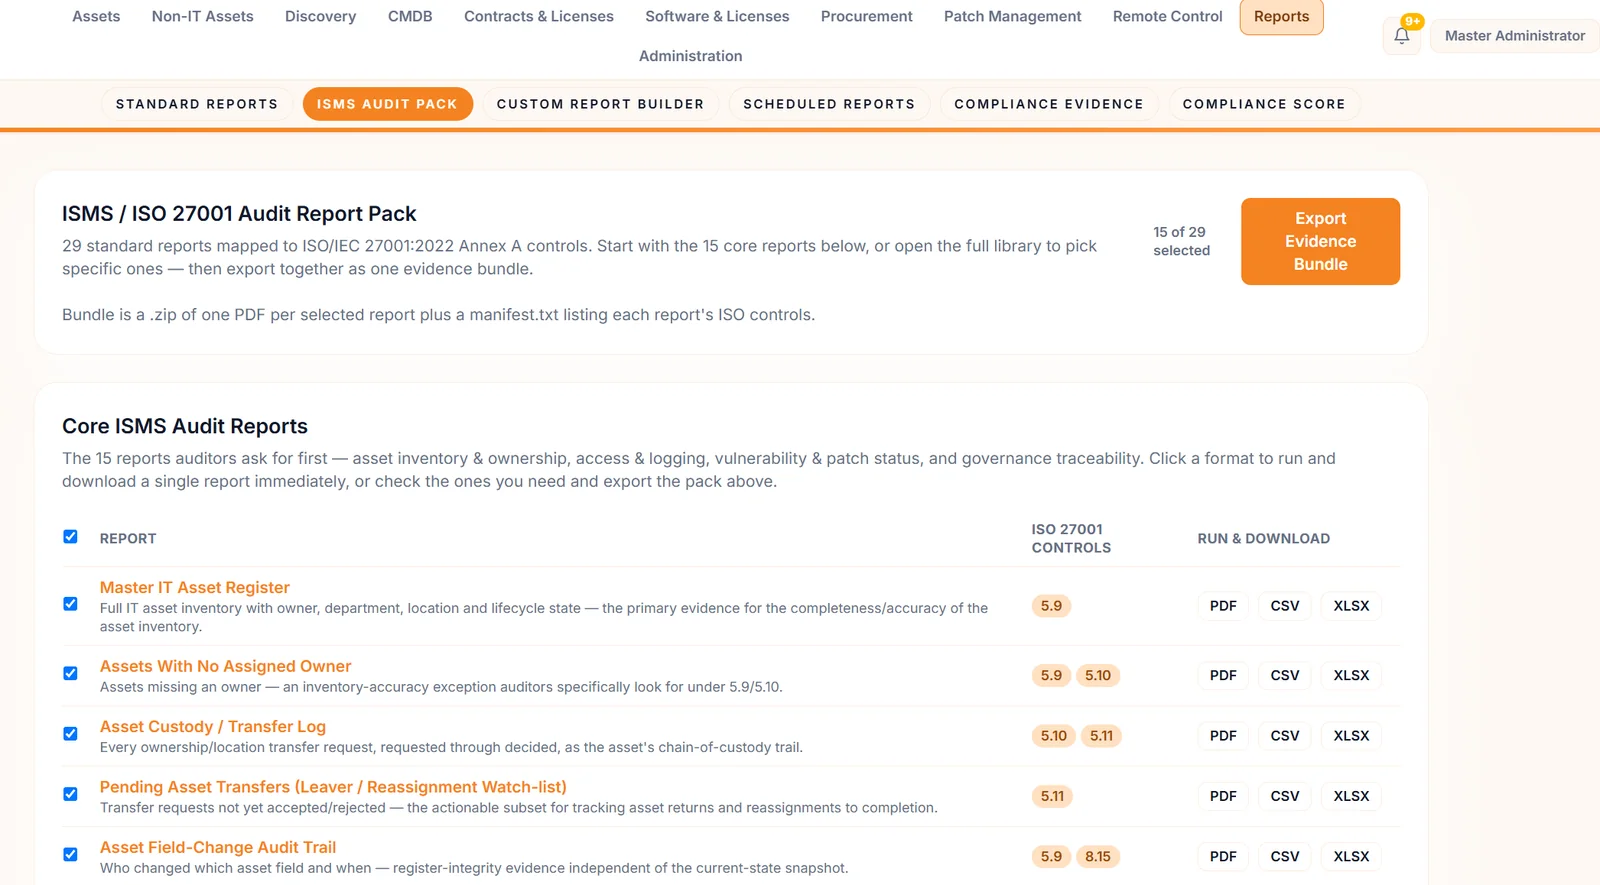
Closed withAn ISMS audit pack of 29 reports, exported as one bundle of PDFs with a manifest, plus reports that can be scheduled to email out on their own.
How it goes wrongYou learn which controls have no evidence when someone else points at the hole.
Closed withA control coverage matrix lists every tracked control as covered or a gap, and uploaded evidence files, stored with a SHA-256 checksum, close gaps you tag to a control.
Evidence on demand
These are the 29 reports in IntelliAsset's ISMS audit pack, with the controls each one maps to. Select the ones an audit needs and watch the control coverage change. Controls no report covers show as gaps.
The 15 core reports are preselected.
ISO/IEC 27001:2022 Annex A controls the platform tracks. A gap is a control no report covers, and you can add uploaded evidence to close it.
Each selected report becomes a PDF in the bundle, listed with its controls.
Report names and control mappings are from IntelliAsset's ISMS audit pack. Selection and uploaded evidence here are illustrative.
Every platform keeps its own trail
The answer to “who did that?” lives where the work happens, and each platform records it.
Who changed a record, and from what to what?
Who did what on the service desk?
Can we prove the trail wasn't altered?
What fired, and what did we do about it?
Illustrative entries. Fields shown are what each platform records. Sample data.
See it live
Screens are from the products running test or sample data.
What changes
The reports auditors ask for first already exist, and an evidence bundle is a few clicks.
The control coverage matrix shows which controls have no evidence before the audit does.
Every asset has an owner on record, and every change has an actor, a time and an approval.
Evidence comes from the systems doing the work, and scheduled reports keep arriving on their own.
Built with
Asset and patch management
The ISMS audit pack, control coverage matrix, evidence repository, patch and asset reports, and scheduled reports.
IT service management
System audit log, CAB approvals, post-implementation reviews, and scheduled reports.
Privileged access management
A hash-chained audit trail, encrypted session recordings and SIEM export.
Operations and observability
Alarm and automation run history, config snapshots with diff, and scheduled reports.
Questions
No tool does that on its own. IntelliAsset produces evidence for the asset-management and technical controls it covers, mapped to ISO/IEC 27001:2022 Annex A, and the control coverage matrix shows the controls it doesn't cover as gaps. Deciding what satisfies a control is still up to you and your auditor.
Of the 33 controls the matrix tracks, 22 have at least one report behind them today, including asset inventory (5.9), user endpoint devices (8.1), technical vulnerabilities (8.8), configuration (8.9), logging (8.15), monitoring (8.16) and network security (8.20). The rest appear as gaps unless you upload evidence and tag it to the control.
A zip file with one PDF for each report you select, plus a manifest that lists each report and the controls it maps to. A default set of 15 core reports is preselected, and you can add any of the 29.
Yes. Evidence files such as VAPT reports, policies and audit reports are stored with a SHA-256 checksum and can be tagged to controls. Tagged evidence counts toward the coverage matrix.
Not all of them are the same. Securita360's audit trail is hash-chained, so changing or deleting an older event is detectable, and events can be exported to your SIEM. IntelliAsset's and ITDesk's audit logs record who did what and when, including IP addresses, but they are not hash-chained.
Yes. IntelliAsset can schedule any report to email out on a timetable, ITDesk has report schedules with recipients and a format, and Unified360 can schedule daily, weekly or monthly reports as PDF.
The report mapping today is to ISO/IEC 27001:2022 Annex A. Evidence files can be categorised as VAPT, ITIL4, CIS, policy or audit report, but other frameworks are not mapped control by control.
IntelliAsset is self-hosted, so inventory, documents and evidence stay inside your network. Securita360 and the other platforms can also run on your own infrastructure.
See it on your own audit
Tell us which framework you're preparing for and we'll show you the evidence Autointelli already keeps, and the gaps it shows. No commitment required.